We are pleased to announce new enhancements to the Customer Management module with the option to enforce DANE (DNS-Based Authentication of Named Entities) validation for the inbound email flow.
Over the next two weeks, we will be enabling the following options:
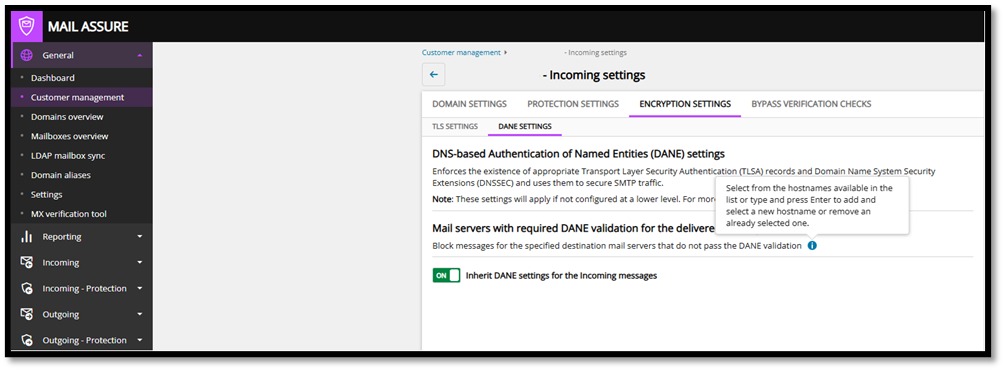
Encryption Settings page has been enhanced with the “DANE Settings” tab-page including the option to enforce the existence of appropriate TLSA (Transport Layer Security Authentication) records and DNSSEC (Domain Name System Security Extensions).
To maintain flexible configuration, DANE enforcement can also be set at the domain level on the Filtering settings page.
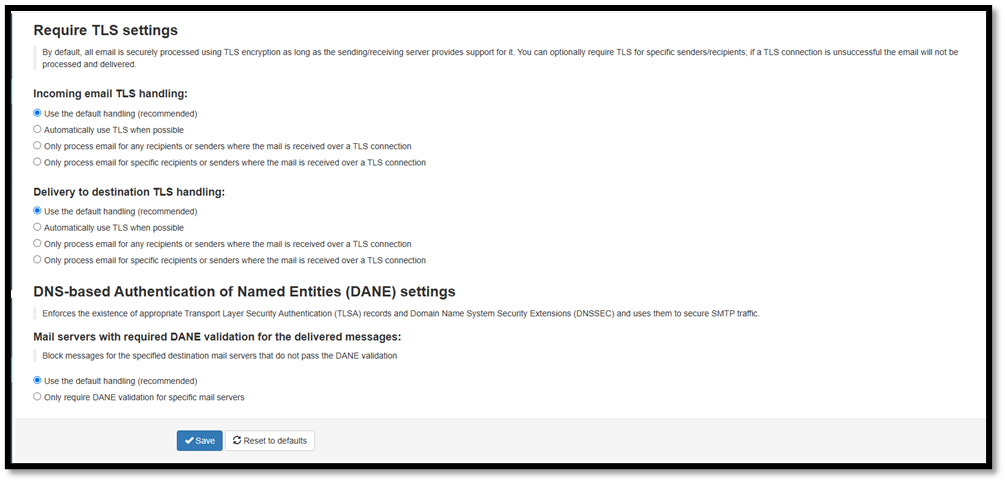
DANE, or DNS-Based Authentication of Named Entities, is a security protocol that utilises the DNS system to establish online communication and verify the authenticity and integrity of secure connections.
TLS relies on Certificate Authorities, but DANE adds security by allowing domain owners to designate trusted certificates.
DANE complements TLS by providing an additional layer of security for email encryption, rather than serving as a replacement.
The new option requires the destination server to support this security protocol. If DANE validation fails, the message will not be delivered.
We’ve also implemented the following improvements:
Since the latest major release, we’ve fixed the following issues:
