
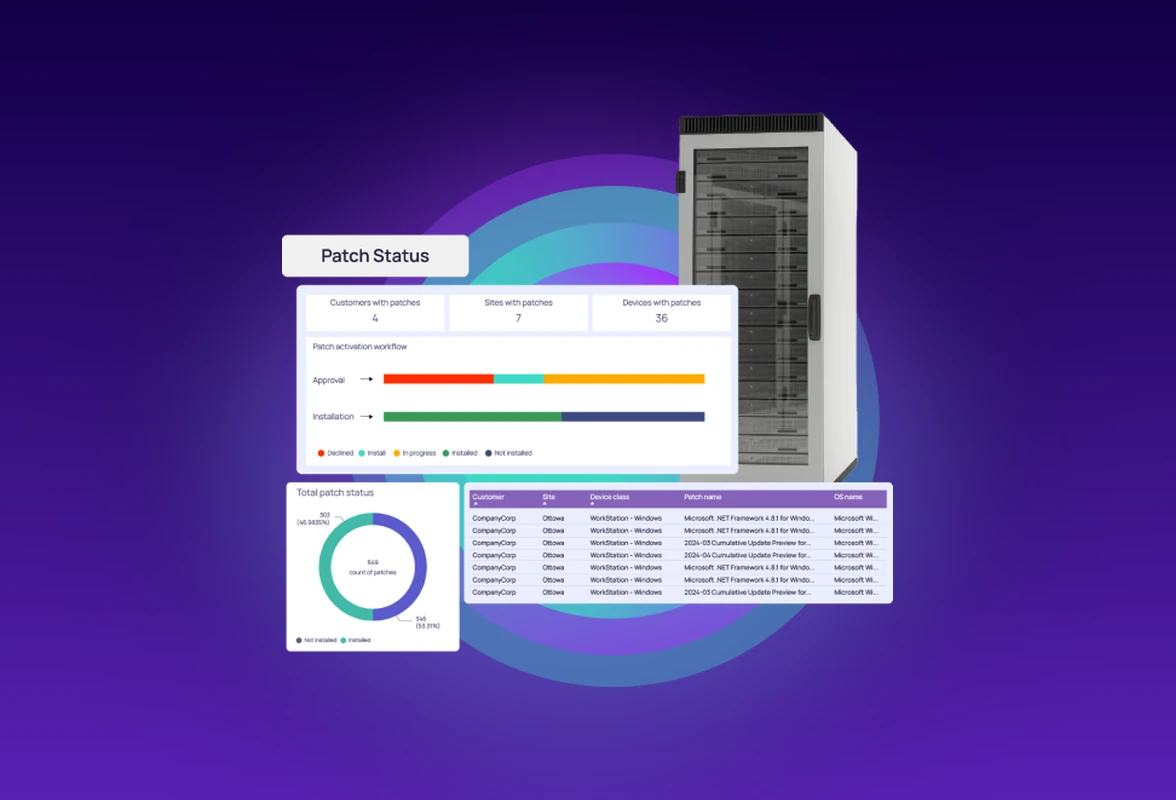
Server Patch Management Patch servers faster. Close vulnerabilities sooner.
Stay ahead of cyberthreats with server patch management from N-able UEM, combining risk-based prioritization, automated workflows, and audit-ready reporting in one console.
Stay ahead of threats with intelligent server patching
One console. Every server OS.
Patch Windows, macOS, and Linux servers from a single console with unified policies, dashboards, and reporting across every OS, no bolt-on tools required.
Prioritize what matters most
N-zo Patch Expert surfaces what to patch and why, using CVSS scores, CISA KEV status, and live server context, so your team focuses on the highest-risk gaps first.
Automate the routine, focus on the critical
Set patch policies that handle scheduling, approvals, retries, and reboot control automatically, keeping server patch completion rates high without manual follow-up.
Stay audit-ready without the extra work
Generate patch compliance reports and server patch history as a byproduct of daily operations, giving you audit-grade evidence without extra documentation work.
Choose the UEM built for your server patching needs
Manage large networks and scale patch operations.
- Cutting-edge security, automation, and integrations
- Scale operations without adding resources
- Achieve peace of mind knowing your devices are secured with reliable patching
Under contract? We've got you covered.
Patch fast with RMM designed for smaller MSPs and IT departments.
- RMM + remote access + ticketing and billing
- Get started in minutes and expand as you grow
- Upgrade from your usual RMM tools with leveled-up patching
A complete solution with easy setup.
Not sure which fits your business better? Read more about how they compare.
FAQs
What is server patch management software?
What is server patch management software?
Server patch management software automates the process of identifying, deploying, and verifying security and software updates across server infrastructure. It helps IT teams and MSPs maintain server security, reduce vulnerabilities, and keep operating systems and applications up to date without manual intervention. N-able UEM integrates this directly into the endpoint management workflow, covering Windows, macOS, and Linux servers from a single console.
How does server patch management reduce exposure windows?
How does server patch management reduce exposure windows?
N-able UEM connects detection, prioritization, and remediation in one continuous workflow. Built-in scanning runs every six hours across Windows, macOS, and Linux. When a vulnerability is identified, you can deploy a patch for 500+ third-party applications directly from the vulnerability view, then trigger an on-demand scan to confirm the fix, compressing exposure from days to minutes.
How does N-able UEM automate server patch management?
How does N-able UEM automate server patch management?
N-able UEM automates server patching through policy-driven workflows that handle scheduling, approvals, retries, offline devices, and reboot control. AI-powered prioritization via N-zo surfaces the highest-risk patches based on CVSS scores, CISA KEV status, and live server context. Patches deploy automatically according to your policies, and on-demand scanning verifies fixes immediately. This helps reduce manual effort, improve completion rates, and close exposure windows faster.
How does N-able UEM help with patch compliance and auditing?
How does N-able UEM help with patch compliance and auditing?
N-able UEM generates patch compliance reports and maintains detailed patch history in Asset View as a byproduct of daily operations. This gives you audit-grade evidence without additional documentation work. You can track patch status, remediation timelines, and completion rates across your server estate, helping simplify compliance audits and customer reporting.
What is the difference between N-central and N-sight for server patching?
What is the difference between N-central and N-sight for server patching?
N-central is built for advanced control, automation, and scale. It offers multi-tenant patch policies, deeper customization, and AI-powered patch prioritization through N-zo, ideal for MSPs managing complex, distributed server environments. N-sight is designed for clarity, simplicity, and speed, with streamlined workflows that help smaller IT teams patch servers quickly without added complexity. Both support Windows, macOS, and Linux server patching from a unified console.
How does AI help with server patching?
How does AI help with server patching?
N-zo prioritizes vulnerabilities by combining CVSS severity, CISA KEV active exploitation status, EPSS probability, and live device context, surfacing the exposures that carry the highest real-world risk. The Patch Expert turns complex patch signals into clear next steps, and AI-assisted scripting translates natural-language requests into ready-to-run scripts.
Does N-able UEM support multi-OS server environments?
Does N-able UEM support multi-OS server environments?
Yes. N-able UEM delivers unified patch management across Windows, macOS, and Linux from one console, with shared policies, dashboards, and reporting. Third-party application patching covers 500+ apps, and Mac and Linux OS patching is fully supported. Windows OS patching within the integrated vulnerability-to-patch workflow is on the roadmap.
Patch servers before attackers exploit them
Start closing risk with AI-powered prioritization, automated policies, and closed-loop verification — all from the same platform you use to manage endpoints.